


Get Ready with PT0-002 Exam Dumps (2024)
Realistic PT0-002 Dumps are Available for Instant Access
The registration process of the CompTIA PT0-002 Certification Exam
The steps to get registered for the PT0-002 Certification Exam, explained in the PT0-002 Dumps are as follows:
Now, you will be redirected to the registration page of the PT0-002 exam, fill in the required details and click on the submit button.
After paying the exam fee, you will receive a confirmation message from the CompTIA. CompTIA PT0-002 Certification Exam is being delivered by the Pearson VUE. You can take it either online or onsite.
Enter the required details in the given fields of the CompTIA website, and After filling in all the required details, click on the submit button.
You will be redirected to the CompTIA's official website, click on the link of the PT0-002 Certification Exam.
Go to the official website of the CompTIA and click on the link to the PT0-002 Certification Exam.
NEW QUESTION # 40
After gaining access to a previous system, a penetration tester runs an Nmap scan against a network with the following results:
The tester then runs the following command from the previous exploited system, which fails:
Which of the following explains the reason why the command failed?
- A. The command requires the-port 135 option.
- B. An account for RDP does not exist on the server.
- C. PowerShell requires administrative privilege.
- D. The tester input the incorrect IP address.
Answer: B
NEW QUESTION # 41
A penetration tester fuzzes an internal server looking for hidden services and applications and obtains the following output: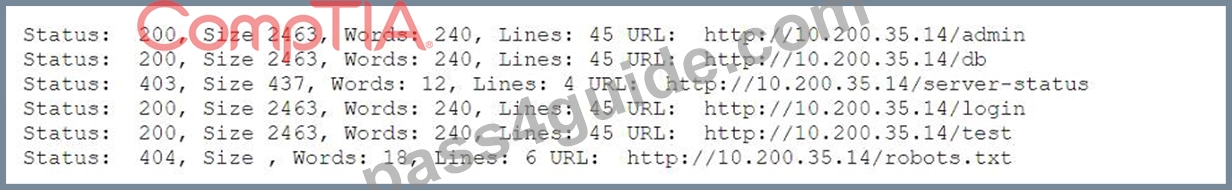
Which of the following is the most likely explanation for the output?
- A. The admin directory cannot be fuzzed because it is forbidden.
- B. The admin, test, and db directories redirect to the log-in page.
- C. The tester does not have credentials to access the server-status page.
- D. The robots.txt file has six entries in it.
Answer: B
Explanation:
The output of the fuzzing tool shows that the admin, test, and db directories have the same size, words, and lines as the login page, which indicates that they are redirecting to the loginpage. This means that the tester cannot access these directories without valid credentials. The server-status page returns a 403 Forbidden status code, which means that the tester does not have permission to access it. The robots.txt file returns a 404 Not Found status code, which means that the file does not exist on the server. References:
*The Official CompTIA PenTest+ Study Guide (Exam PT0-002), Chapter 2: Conducting Passive Reconnaissance, page 77-78.
*101 Labs - CompTIA PenTest+: Hands-on Labs for the PT0-002 Exam, Lab 2.3: Fuzzing Web Applications, page 69-70.
NEW QUESTION # 42
A penetration tester conducted a discovery scan that generated the following:
Which of the following commands generated the results above and will transform them into a list of active hosts for further analysis?
- A. nmap -o 192.168.0.1-254, cut -f 2
- B. nmap -sn 192.168.0.1-254 , grep "Nmap scan" | awk '{print S5}'
- C. nmap -oG list.txt 192.168.0.1-254 , sort
- D. nmap --open 192.168.0.1-254, uniq
Answer: A
NEW QUESTION # 43
A company recently moved its software development architecture from VMs to containers. The company has asked a penetration tester to determine if the new containers are configured correctly against a DDoS attack.
Which of the following should a tester perform first?
- A. Perform a vulnerability check against the hypervisor.
- B. Test the strength of the encryption settings.
- C. Determine if security tokens are easily available.
- D. .Scan the containers for open ports.
Answer: D
Explanation:
Explanation
The first step that a tester should perform to determine if the new containers are configured correctly against a DDoS attack is to scan the containers for open ports. Open ports are entry points for network communication and can expose services or applications that may be vulnerable to DDoS attacks. Scanning the containers for open ports can help the tester identify which services or applications are running on the containers, and which ones may need to be secured or disabled to prevent DDoS attacks. Scanning the containers for open ports can also help the tester discover any unauthorized or malicious services or applications that may have been installed on the containers by previous attackers or compromised containers. Scanning the containers for open ports can be done by using tools such as Nmap, which can perform network scanning and enumeration by sending packets to hosts and analyzing their responses1. The other options are not the first steps that a tester should perform to determine if the new containers are configured correctly against a DDoS attack. Testing the strength of the encryption settings is not relevant to DDoS attacks, as encryption does not prevent or mitigate DDoS attacks, but rather protects data confidentiality and integrity. Determining if security tokens are easily available is not relevant to DDoS attacks, as security tokens are used for authentication and authorization, not for preventing or mitigating DDoS attacks. Performing a vulnerability check against the hypervisor is not relevant to DDoS attacks, as the hypervisor is not directly exposed to network traffic, but rather manages the virtual machines or containers that run on it.
NEW QUESTION # 44
A penetration tester who is conducting a web-application test discovers a clickjacking vulnerability associated with a login page to financial data. Which of the following should the tester do with this information to make this a successful exploit?
- A. Use browser autopwn.
- B. Perform XSS.
- C. Conduct a watering-hole attack.
- D. Use BeEF.
Answer: C
Explanation:
A clickjacking vulnerability allows an attacker to trick a user into clicking on a hidden element on a web page, such as a login button or a link. A watering-hole attack is a technique where the attacker compromises a website that is frequently visited by the target users, and injects malicious code or content into the website.
The attacker can then use the clickjacking vulnerability to redirect the users to a malicious website or perform unauthorized actions on their behalf.
A: Perform XSS. This is incorrect. XSS (cross-site scripting) is a vulnerability where an attacker injects malicious scripts into a web page that are executed by the browser of the victim. XSS can be used to steal cookies, session tokens, or other sensitive information, but it is not directly related to clickjacking.
C: Use BeEF. This is incorrect. BeEF (Browser Exploitation Framework) is a tool that allows an attacker to exploit various browser vulnerabilities and take control of the browser of the victim. BeEF can be used to launch clickjacking attacks, but it is not the only way to do so.
D: Use browser autopwn. This is incorrect. Browser autopwn is a feature of Metasploit that automatically exploits browser vulnerabilities and delivers a payload to the victim's system. Browser autopwn can be used to compromise the browser of the victim, but it is not directly related to clickjacking.
References:
* 1: OWASP Foundation, "Clickjacking", https://owasp.org/www-community/attacks/Clickjacking
* 2: PortSwigger, "What is clickjacking? Tutorial & Examples",
https://portswigger.net/web-security/clickjacking
* 4: Akto, "Clickjacking: Understanding vulnerability, attacks and prevention",
https://www.akto.io/blog/clickjacking-understanding-vulnerability-attacks-and-prevention
NEW QUESTION # 45
A penetration tester performs the following command:
curl -I -http2 https://www.comptia.org
Which of the following snippets of output will the tester MOST likely receive?
- A. Option C
- B. Option A
- C. Option D
- D. Option B
Answer: B
NEW QUESTION # 46
The following line-numbered Python code snippet is being used in reconnaissance:
Which of the following line numbers from the script MOST likely contributed to the script triggering a
"probable port scan" alert in the organization's IDS?
- A. Line 02
- B. Line 08
- C. Line 07
- D. Line 01
Answer: B
NEW QUESTION # 47
A company is concerned that its cloud service provider is not adequately protecting the VMs housing its software development. The VMs are housed in a datacenter with other companies sharing physical resources.
Which of the following attack types is MOST concerning to the company?
- A. Cybersquatting
- B. Side channel
- C. Session riding
- D. Data flooding
Answer: B
Explanation:
https://www.techtarget.com/searchsecurity/definition/side-channel-attack#:~:text=Side%2Dchannel%20attacks%
NEW QUESTION # 48
A penetration tester is conducting an engagement against an internet-facing web application and planning a phishing campaign. Which of the following is the BEST passive method of obtaining the technical contacts for the website?
- A. WHOIS domain lookup
- B. SSL certificate information
- C. Public data breach dumps
- D. Job listing and recruitment ads
Answer: A
Explanation:
The BEST passive method of obtaining the technical contacts for the website would be a WHOIS domain lookup. WHOIS is a protocol that provides information about registered domain names, such as the registration date, registrant's name and contact information, and the name servers assigned to the domain. By performing a WHOIS lookup, the penetration tester can obtain the contact information of the website's technical staff, which can be used to craft a convincing phishing email.
NEW QUESTION # 49
During a client engagement, a penetration tester runs the following Nmap command and obtains the following output:
nmap -sV -- script ssl-enum-ciphers -p 443 remotehost
| TLS_ECDHE_ECDSA_WITH_RC4_128_SHA
| TLS_ECDHE_RSA_WITH_RC4_128_SHA
| TLS_RSA_WITH_RC4_128_SHA (rsa 2048)
TLS_RSA_WITH_RC4_128_MD5 (rsa 2048)
Which of the following should the penetration tester include in the report?
- A. This server should be upgraded to TLS 1.2.
- B. Old, insecure ciphers are in use.
- C. The 3DES algorithm should be deprecated.
- D. 2,048-bit symmetric keys are incompatible with MD5.
Answer: B
NEW QUESTION # 50
You are a security analyst tasked with hardening a web server.
You have been given a list of HTTP payloads that were flagged as malicious.
INSTRUCTIONS
Given the following attack signatures, determine the attack type, and then identify the associated remediation to prevent the attack in the future.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Answer:
Explanation:
Explanation:
1. Reflected XSS - Input sanitization (<> ...)
2. Sql Injection Stacked - Parameterized Queries
3. DOM XSS - Input Sanitization (<> ...)
4. Local File Inclusion - sandbox req
5. Command Injection - sandbox req
6. SQLi union - paramtrized queries
7. SQLi error - paramtrized queries
8. Remote File Inclusion - sandbox
9. Command Injection - input saniti $
10. URL redirect - prevent external calls
NEW QUESTION # 51
A penetration tester opened a shell on a laptop at a client's office but is unable to pivot because of restrictive ACLs on the wireless subnet. The tester is also aware that all laptop users have a hard-wired connection available at their desks. Which of the following is the BEST method available to pivot and gain additional access to the network?
- A. Set up another access point and perform an evil twin attack.
- B. Span deauthentication packets to the wireless clients.
- C. Capture handshakes from wireless clients to crack.
- D. Set up a captive portal with embedded malicious code.
Answer: B
Explanation:
Explanation
The best method available to pivot and gain additional access to the network is to span deauthentication packets to the wireless clients. This will cause them to disconnect from their wireless access point and reconnect using their hard-wired connection, which may have less restrictive ACLs. The penetration tester can then capture their traffic or attempt to compromise their systems.
NEW QUESTION # 52
Which of the following would assist a penetration tester the MOST when evaluating the susceptibility of top-level executives to social engineering attacks?
- A. Scraping social media for personal details
- B. Crawling the company's website for company information
- C. Identifying technical contacts at the company
- D. Registering domain names that are similar to the target company's
Answer: A
Explanation:
Explanation
Scraping social media for personal details can help a penetration tester craft personalized and convincing social engineering attacks against top-level executives, who may share sensitive or confidential information on their profiles. Registering domain names that are similar to the target company's can be used for phishing or typosquatting attacks, but not specifically against executives. Identifying technical contacts at the company can help with reconnaissance, but not with social engineering. Crawling the company's website for company information can provide general background knowledge, but not specific details about executives.
NEW QUESTION # 53
Which of the following tools provides Python classes for interacting with network protocols?
- A. Empire
- B. Responder
- C. PowerSploit
- D. Impacket
Answer: D
NEW QUESTION # 54
For a penetration test engagement, a security engineer decides to impersonate the IT help desk. The security engineer sends a phishing email containing an urgent request for users to change their passwords and a link to
https://example.com/index.html. The engineer has designed the attack so that once the users enter the credentials, the index.html page takes the credentials and then forwards them to another server that the security engineer is controlling. Given the following information:
Which of the following lines of code should the security engineer add to make the attack successful?
- A. redirectUrl = 'https://example.com'
- B. window.location.= 'https://evilcorp.com'
- C. geturlparameter ('username')
- D. crossDomain: true
Answer: D
NEW QUESTION # 55
A consultant is reviewing the following output after reports of intermittent connectivity issues:
? (192.168.1.1) at 0a:d1:fa:b1:01:67 on en0 ifscope [ethernet]
? (192.168.1.12) at 34:a4:be:09:44:f4 on en0 ifscope [ethernet]
? (192.168.1.17) at 92:60:29:12:ac:d2 on en0 ifscope [ethernet]
? (192.168.1.34) at 88:de:a9:12:ce:fb on en0 ifscope [ethernet]
? (192.168.1.136) at 0a:d1:fa:b1:01:67 on en0 ifscope [ethernet]
? (192.168.1.255) at ff:ff:ff:ff:ff:ff on en0 ifscope [ethernet]
? (224.0.0.251) at 01:02:5e:7f:ff:fa on en0 ifscope permanent [ethernet]
? (239.255.255.250) at ff:ff:ff:ff:ff:ff on en0 ifscope permanent [ethernet]
Which of the following is MOST likely to be reported by the consultant?
- A. A multicast session was initiated using the wrong multicast group.
- B. A device on the network has poisoned the ARP cache.
- C. A device on the network has an IP address in the wrong subnet.
- D. An ARP flooding attack is using the broadcast address to perform DDoS.
Answer: B
Explanation:
The gateway for the network (192.168.1.1) is at 0a:d1:fa:b1:01:67, and then, another machine (192.168.1.136) also claims to be on the same MAC address. With this on the same network, intermittent connectivity will be inevitable as along as the gateway remains unreachable on the IP known by the others machines on the network, and given that the new machine claiming to be the gateway has not been configured to route traffic.
The output shows an ARP table that contains entries for IP addresses and their corresponding MAC addresses on a local network interface (en0). ARP stands for Address Resolution Protocol and is used to map IP addresses to MAC addresses on a network. However, one entry in the table is suspicious:
? (192.168.1.136) at 0a:d1:fa:b1:01:67 on en0 ifscope [ethernet]
This entry has the same MAC address as another entry:
? (192.168.1.1) at 0a:d1:fa:b1:01:67 on en0 ifscope [ethernet]
This indicates that a device on the network has poisoned the ARP cache by sending false ARP replies that associate its MAC address with multiple IP addresses, including 192.168.1.136 and 192.168.1.1 (which is likely the gateway address). This allows the device to intercept or redirect traffic intended for those IP addresses.
NEW QUESTION # 56
A compliance-based penetration test is primarily concerned with:
- A. bypassing protection on edge devices.
- B. determining the efficacy of a specific set of security standards.
- C. obtaining specific information from the protected network.
- D. obtaining Pll from the protected network.
Answer: B
NEW QUESTION # 57
Which of the following would MOST likely be included in the final report of a static application-security test that was written with a team of application developers as the intended audience?
- A. Code context for instances of unsafe type-casting operations
- B. Executive summary of the penetration-testing methods used
- C. Bill of materials including supplies, subcontracts, and costs incurred during assessment
- D. Quantitative impact assessments given a successful software compromise
Answer: A
Explanation:
Code context for instances of unsafe type-casting operations would most likely be included in the final report of a static application-security test that was written with a team of application developers as the intended audience, as it would provide relevant and actionable information for the developers to fix the vulnerabilities. Type-casting is the process of converting one data type to another, such as an integer to a string. Unsafe type-casting can lead to errors, crashes, or security issues, such as buffer overflows or code injection.
NEW QUESTION # 58
During a penetration tester found a web component with no authentication requirements. The web component also allows file uploads and is hosted on one of the target public web the following actions should the penetration tester perform next?
- A. Notify the primary contact immediately.
- B. Continue the assessment and mark the finding as critical.
- C. Attempting to remediate the issue temporally.
- D. Shutting down the web server until the assessment is finished
Answer: A
Explanation:
Explanation
The penetration tester should notify the primary contact immediately, as this is a serious security issue that may compromise the confidentiality, integrity, and availability of the web server and its data. A web component with no authentication requirements and file upload capabilities can allow an attacker to upload malicious files, such as web shells, backdoors, or malware, to the web server and gain remote access or execute arbitrary commands on the web server. This can lead to further attacks, such as data theft, data corruption, privilege escalation, lateral movement, or denial of service. The penetration tester should inform the primary contact of the issue and its potential impact, and provide recommendations for remediation, such as implementing authentication mechanisms, restricting file upload types and sizes, or scanning uploaded files for malware. The other options are not appropriate actions for the penetration tester at this stage. Continuing the assessment and marking the finding as critical would delay the notification and remediation of the issue, which may increase the risk of exploitation by other attackers. Attempting to remediate the issue temporarily would interfere with the normal operation of the web server and may cause unintended consequences or damage. Shutting down the web server until the assessment is finished would disrupt the availability of the web server and its services, and may violate the scope or agreement of the assessment.
NEW QUESTION # 59
The attacking machine is on the same LAN segment as the target host during an internal penetration test.
Which of the following commands will BEST enable the attacker to conduct host delivery and write the discovery to files without returning results of the attack machine?
- A. nmap PnsV OiL target.txt A target_text_Service
- B. nmap snn exclude 10.1.1.15 10.1.1.0/24 oA target_txt
- C. nmap iR10oX out.xml | grep Nmap | cut d "f5 > live-hosts.txt
- D. nmap sSPn n iL target.txt A target_txtl
Answer: B
Explanation:
According to the Official CompTIA PenTest+ Self-Paced Study Guide1, the correct answer is A. nmap -sn -n
-exclude 10.1.1.15 10.1.1.0/24 -oA target_txt.
This command will perform a ping scan (-sn) without reverse DNS resolution (-n) on the IP range 10.1.1.0/24, excluding the attack machine's IP address (10.1.1.15) from the scan (-exclude). It will also output the results in three formats (normal, grepable and XML) with a base name of target_txt (-oA).
NEW QUESTION # 60
A penetration tester gives the following command to a systems administrator to execute on one of the target servers:
rm -f /var/www/html/G679h32gYu.php
Which of the following BEST explains why the penetration tester wants this command executed?
- A. To remove a web shell after the penetration test
- B. To close down a reverse shell
- C. To delete credentials the tester created
- D. To trick the systems administrator into installing a rootkit
Answer: A
NEW QUESTION # 61
......
Download Exam PT0-002 Practice Test Questions with 100% Verified Answers: https://vcepractice.pass4guide.com/PT0-002-dumps-questions.html